Cyber threat monitoring platform for everyone

Hunt threats before they find you

Mirsad is an AI-powered platform that continuously monitors dark web forums, Telegram channels, infostealer logs, and leaked databases across 100+ sources to detect compromised credentials and brand threats targeting your organization, in real time.

Your data is visible to you only. Never to another client. Our commitments

100+
Monitored Sources
24/7
Continuous Monitoring
Free, no account needed

Check your exposure, instant answer

We look up the address or domain in the combolists and infostealer logs we monitor. The report is emailed instantly to the checked address (for a company, as soon as the professional address is validated) and is never displayed on this page.

I am checking:

Aggregated report for your domain: compromised machines and combolist entries detected. A validation link is first sent to your professional address, to prove it belongs to you.

3 checks per day. What we do with your data

To be warned of the next leaks automatically: see the plans and pricing

Confidentiality, a value before a feature

Monitoring data leaks comes with a simple rule: never create a new one. At Mirsad, information about a person or a company is shown to them only.

Each to their own scope
An organization only sees what concerns its domains. An individual only sees their own identities. No one else has access.
Nothing is displayed publicly
The free check sends its result to the checked address only, never on screen.
Proof before access
The details of a leak are only revealed once you have proven that the address, the domain or the number belongs to you.
Only what is necessary
Passwords found are partially masked: enough to act, not to be reused.
Never sold, never shared
We do not sell your data and do not share it with any third party. If a service provider (MSSP) runs the monitoring on your behalf, its analysts only get access with your explicit consent.

More than 100 sources, monitored continuously

Forums, marketplaces, channels and groups linked to cybercrime, selected by our team and collected around the clock.

  • Credentials stolen from infected machines. We automatically match them against your domains.

    480,000
    Infostealer logs collected in October 2026

    One log is the data extracted from one infected machine.

  • Lists of logins and passwords circulated after data breaches. Automatic matching against your domains.

    1.2 billion
    Combolist entries collected in October 2026

    One entry is a login and password pair found in a circulated list.

  • Sales of access and data. AI agents spot mentions of your organization, your executives and your intellectual property.

  • Data sales, claims, brand impersonation and chatter between threat actors.

In addition, we map your exposed surface: subdomains, certificates, open ports and misconfigurations.

Every dark web and social network post is kept as a screenshot, with up to 3 years of history: if the source disappears, the alert keeps its proof.

How a source enters our scope

  1. 1
    Discovery

    OSINT monitoring and suggestions from our clients.

  2. 2
    Vetting

    The Mirsad team validates its relevance for cybersecurity.

  3. 3
    Monitoring

    Continuous collection as soon as it is validated.

Compromised machines over the last 6 months

Distinct machines per country, counted by hardware identifier.

The 10 most affected countries

  1. 1IN 729,000
  2. 2US 101,000
  3. 3BR 78,000
  4. 4BD 71,000
  5. 5PH 70,000
  6. 6ID 68,000
  7. 7VN 48,000
  8. 8PK 42,000
  9. 9FR 40,000
  10. 10TR 33,000

AI Agents + Human Expertise

The AI handles the volume, our analysts decide. Step by step, who does what.

Split of the work between the AI agents and the analysts, step by step
Processed by AI Verified by our analysts
Collection
Continuous collection on more than 100 sources: forums, marketplaces, Telegram channels, infostealer logs and leaked databases. Select each source and validate its relevance before it enters the scope.
Analysis
Classifies dark web and social network posts, and matches stolen credentials against your domains. Review each detection of the AI agents and filter out false positives before it reaches you.
Alerting
Notifies you as soon as a threat is confirmed, by email or by webhook to your SIEM or SOAR. Support you according to your level: Standard, Priority, or Premium with on-call incident response.

The product, as your analysts see it

Screenshots taken on a demonstration environment: all the data shown is fictitious.

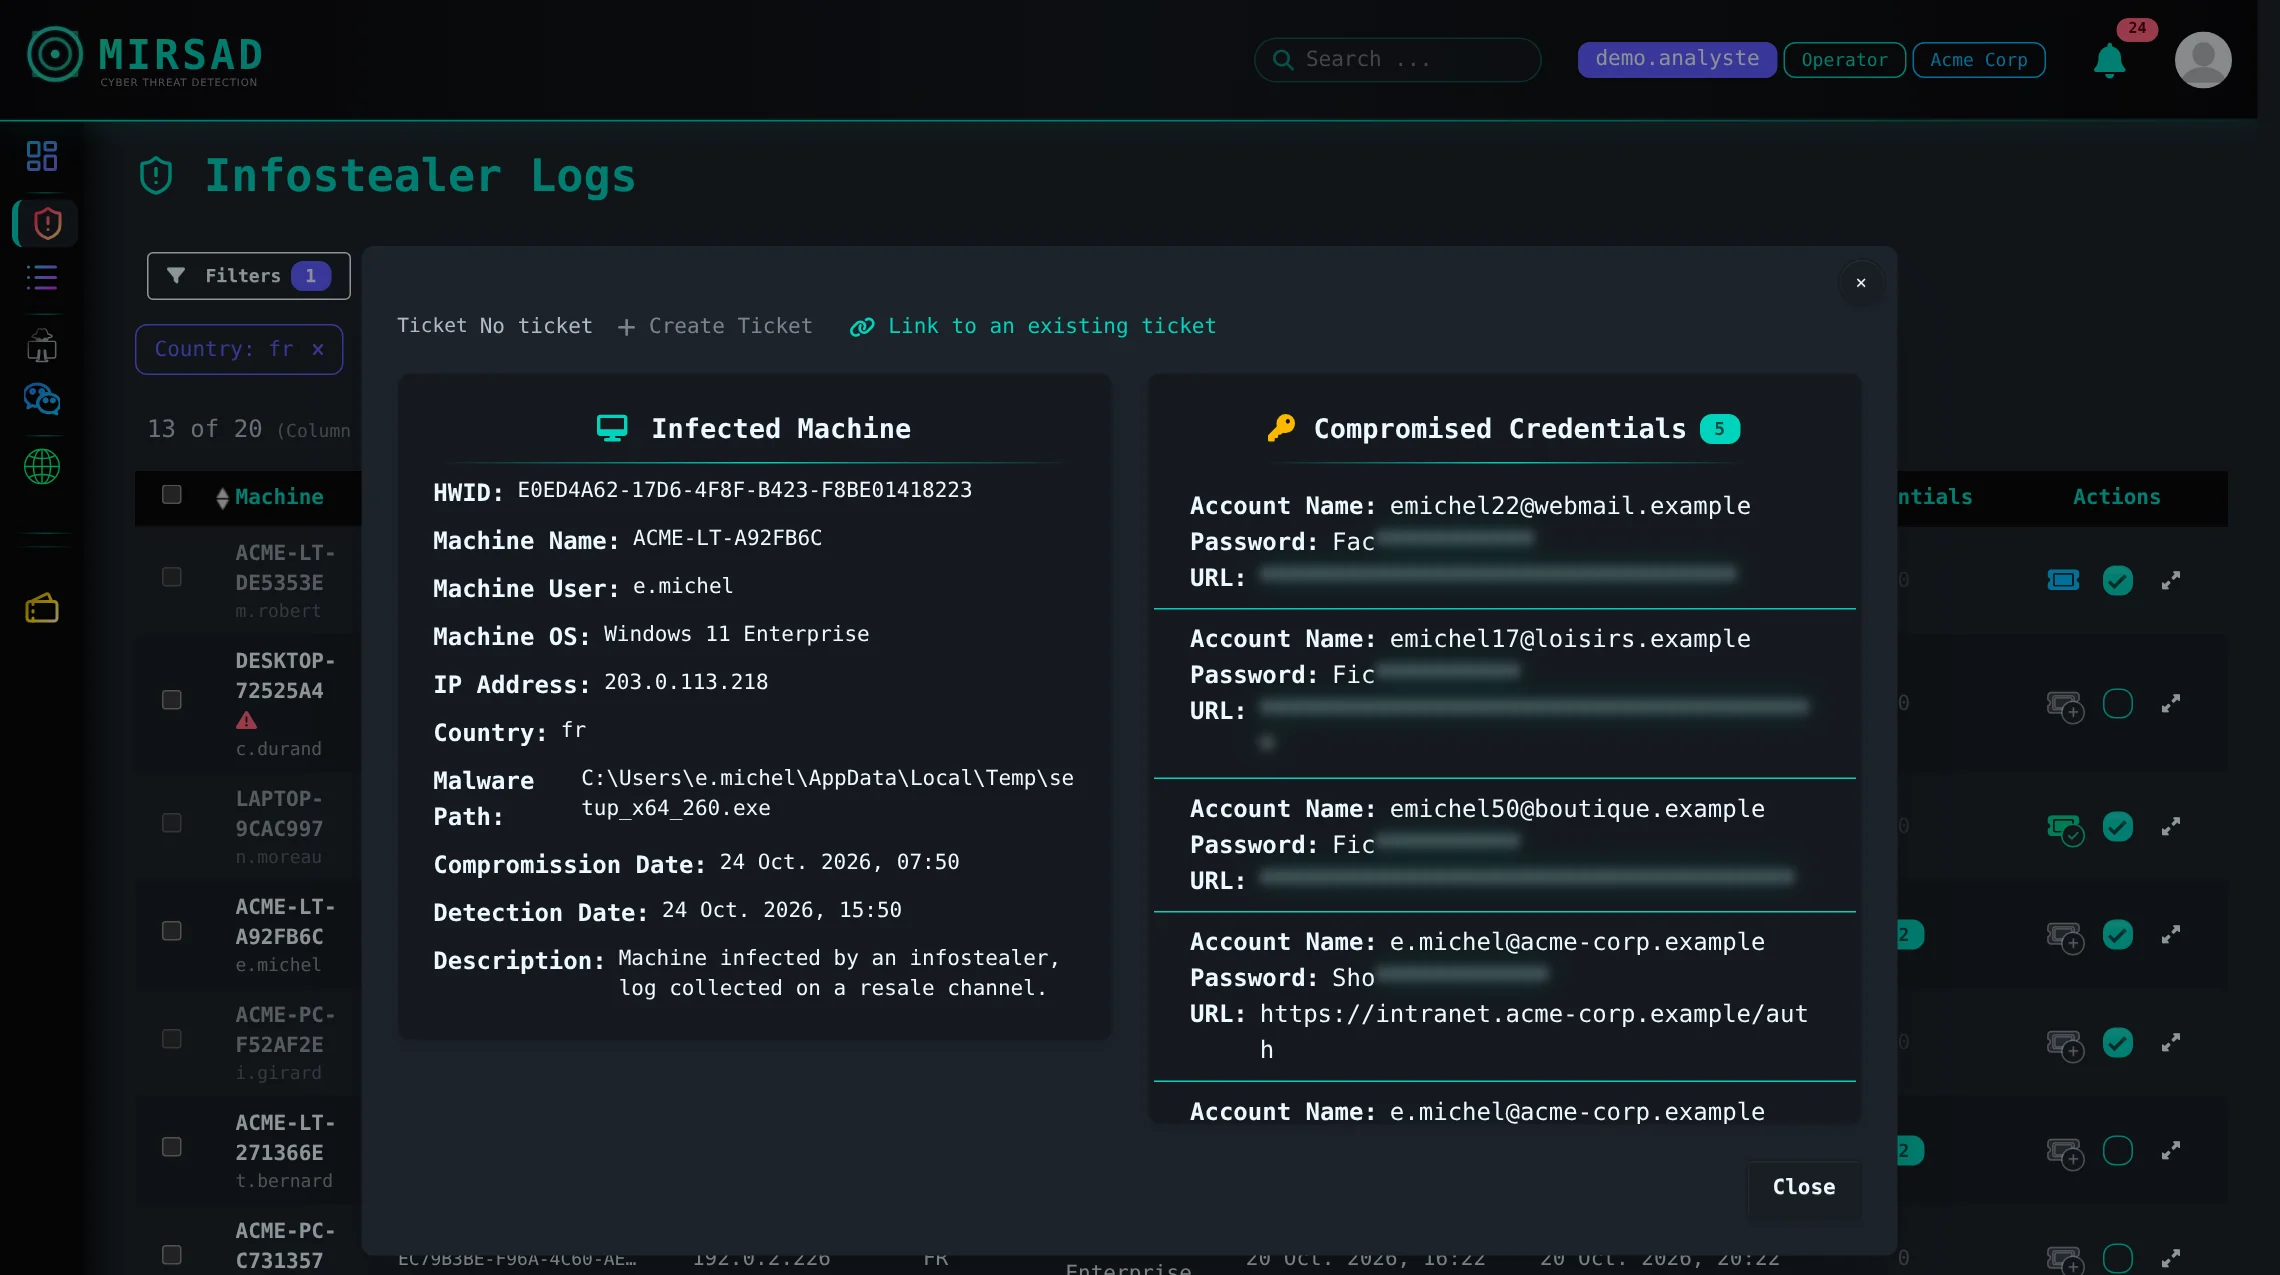
Every infected machine, in detail

For each machine: the user, the system, the malware and the credentials stolen on your domains. You know which account to reset and which machine to act on.

  1. 1 The infected machine: user, system, IP address, malware path
  2. 2 The stolen credentials, password partly masked
  3. 3 Outside your scope, the URL stays masked
Compromises list in Mirsad, then the detail of an infected machine and its stolen credentials

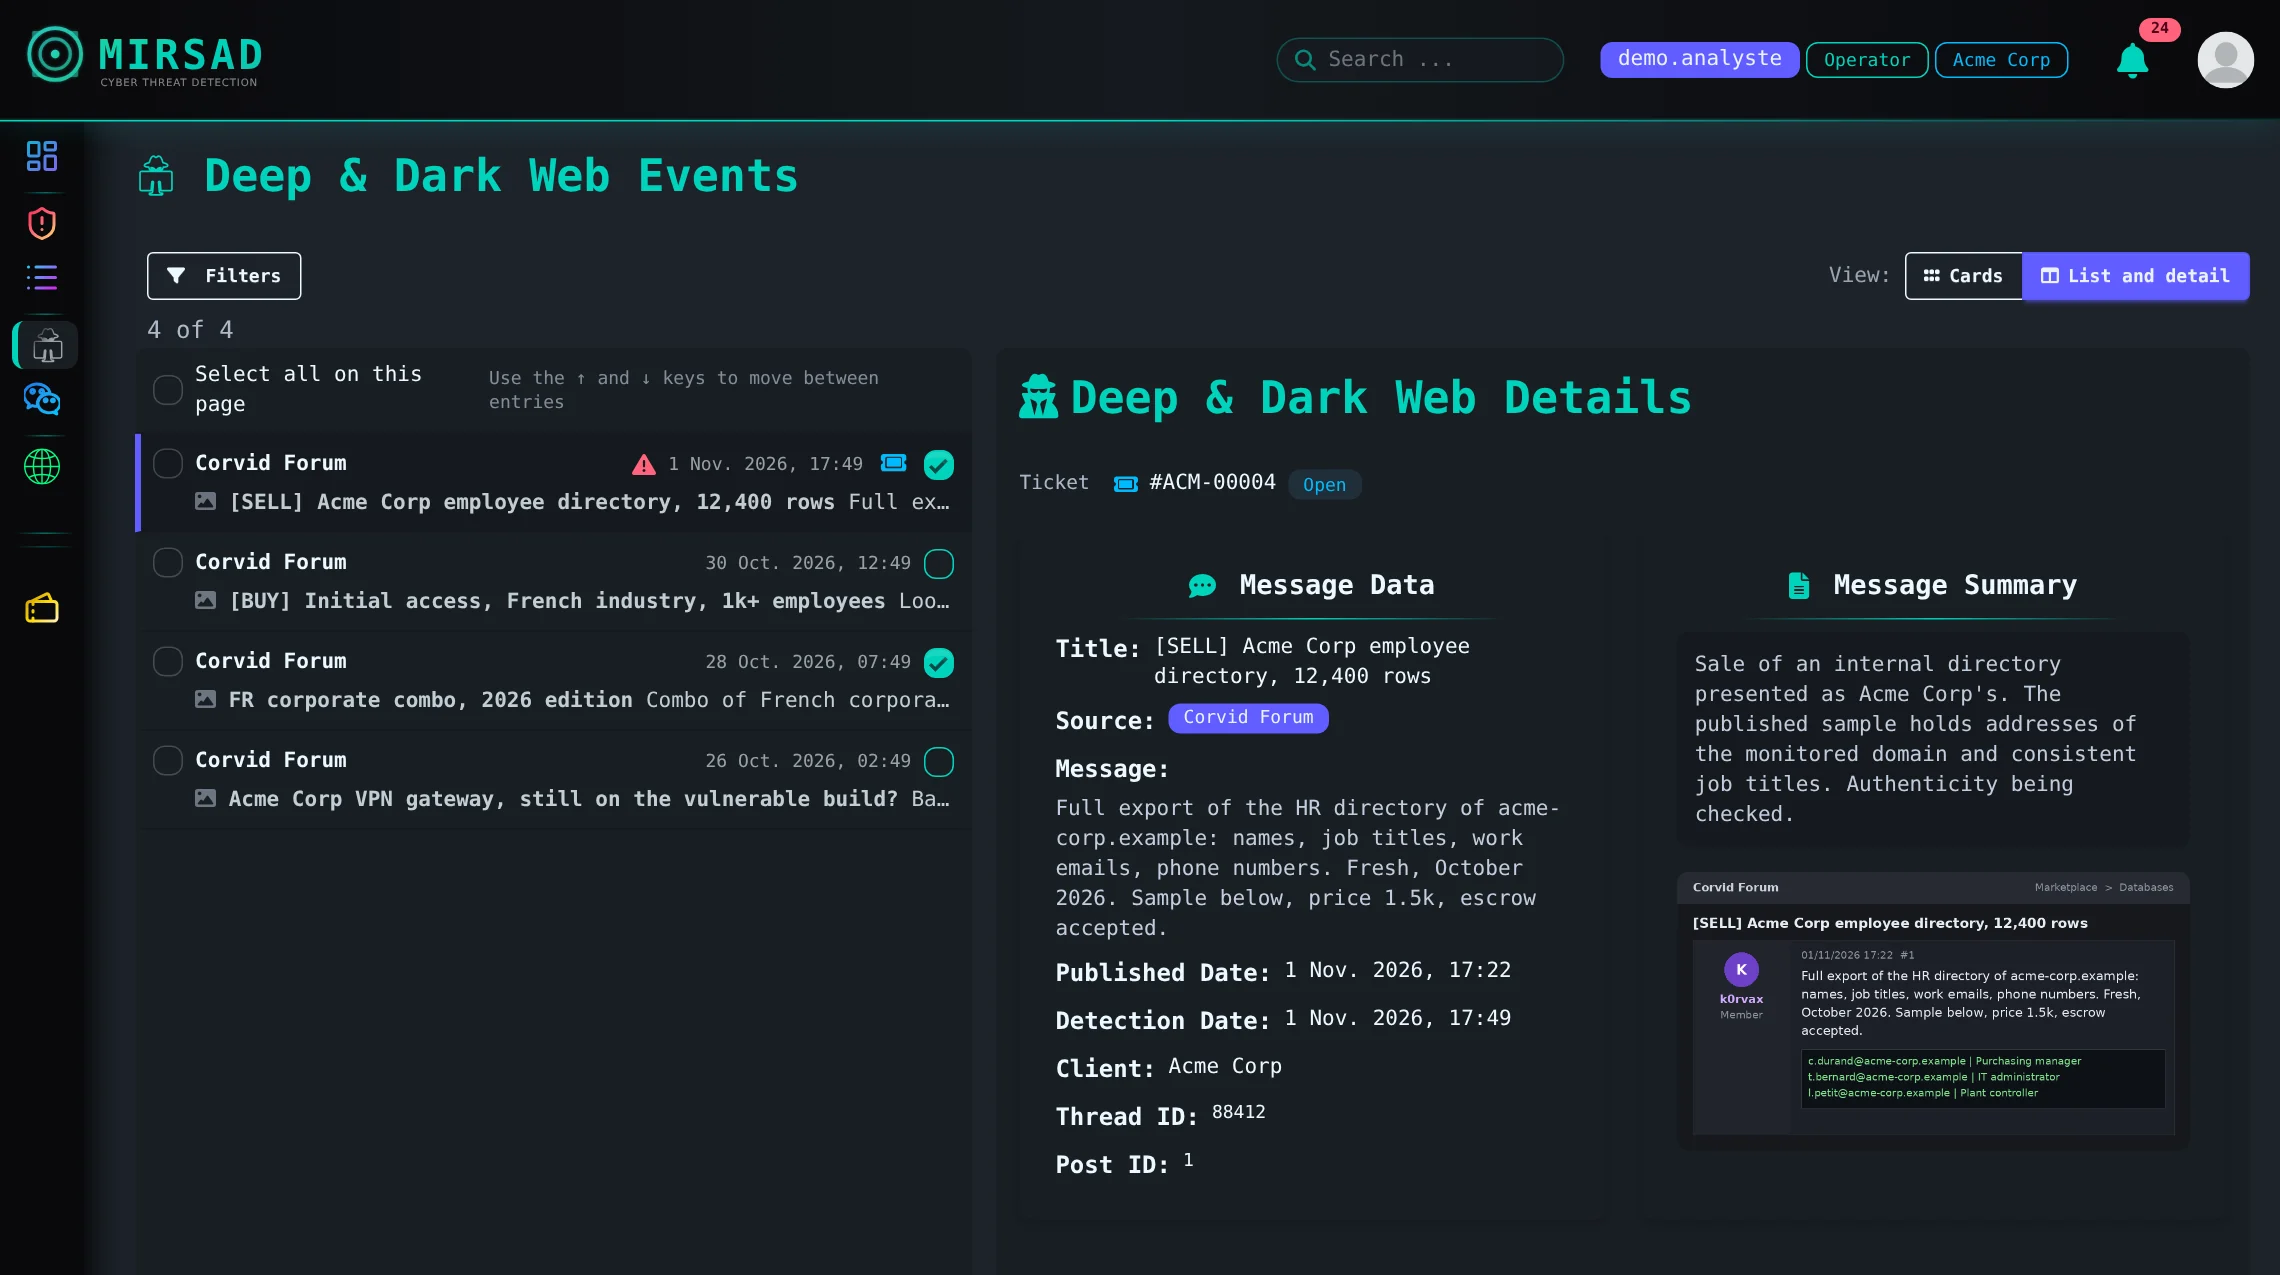
The proof stays, even when the source disappears

Each dark web alert keeps the original post, the analyst summary and a screenshot of the post. A deleted thread or a closed forum does not erase your alert.

  1. 1 The alert ticket and its state
  2. 2 The forum thread, its source and the original message
  3. 3 The analysis summary and the screenshot of the post
Dark web alerts in Mirsad, list and detail side by side, with the screenshot of the post

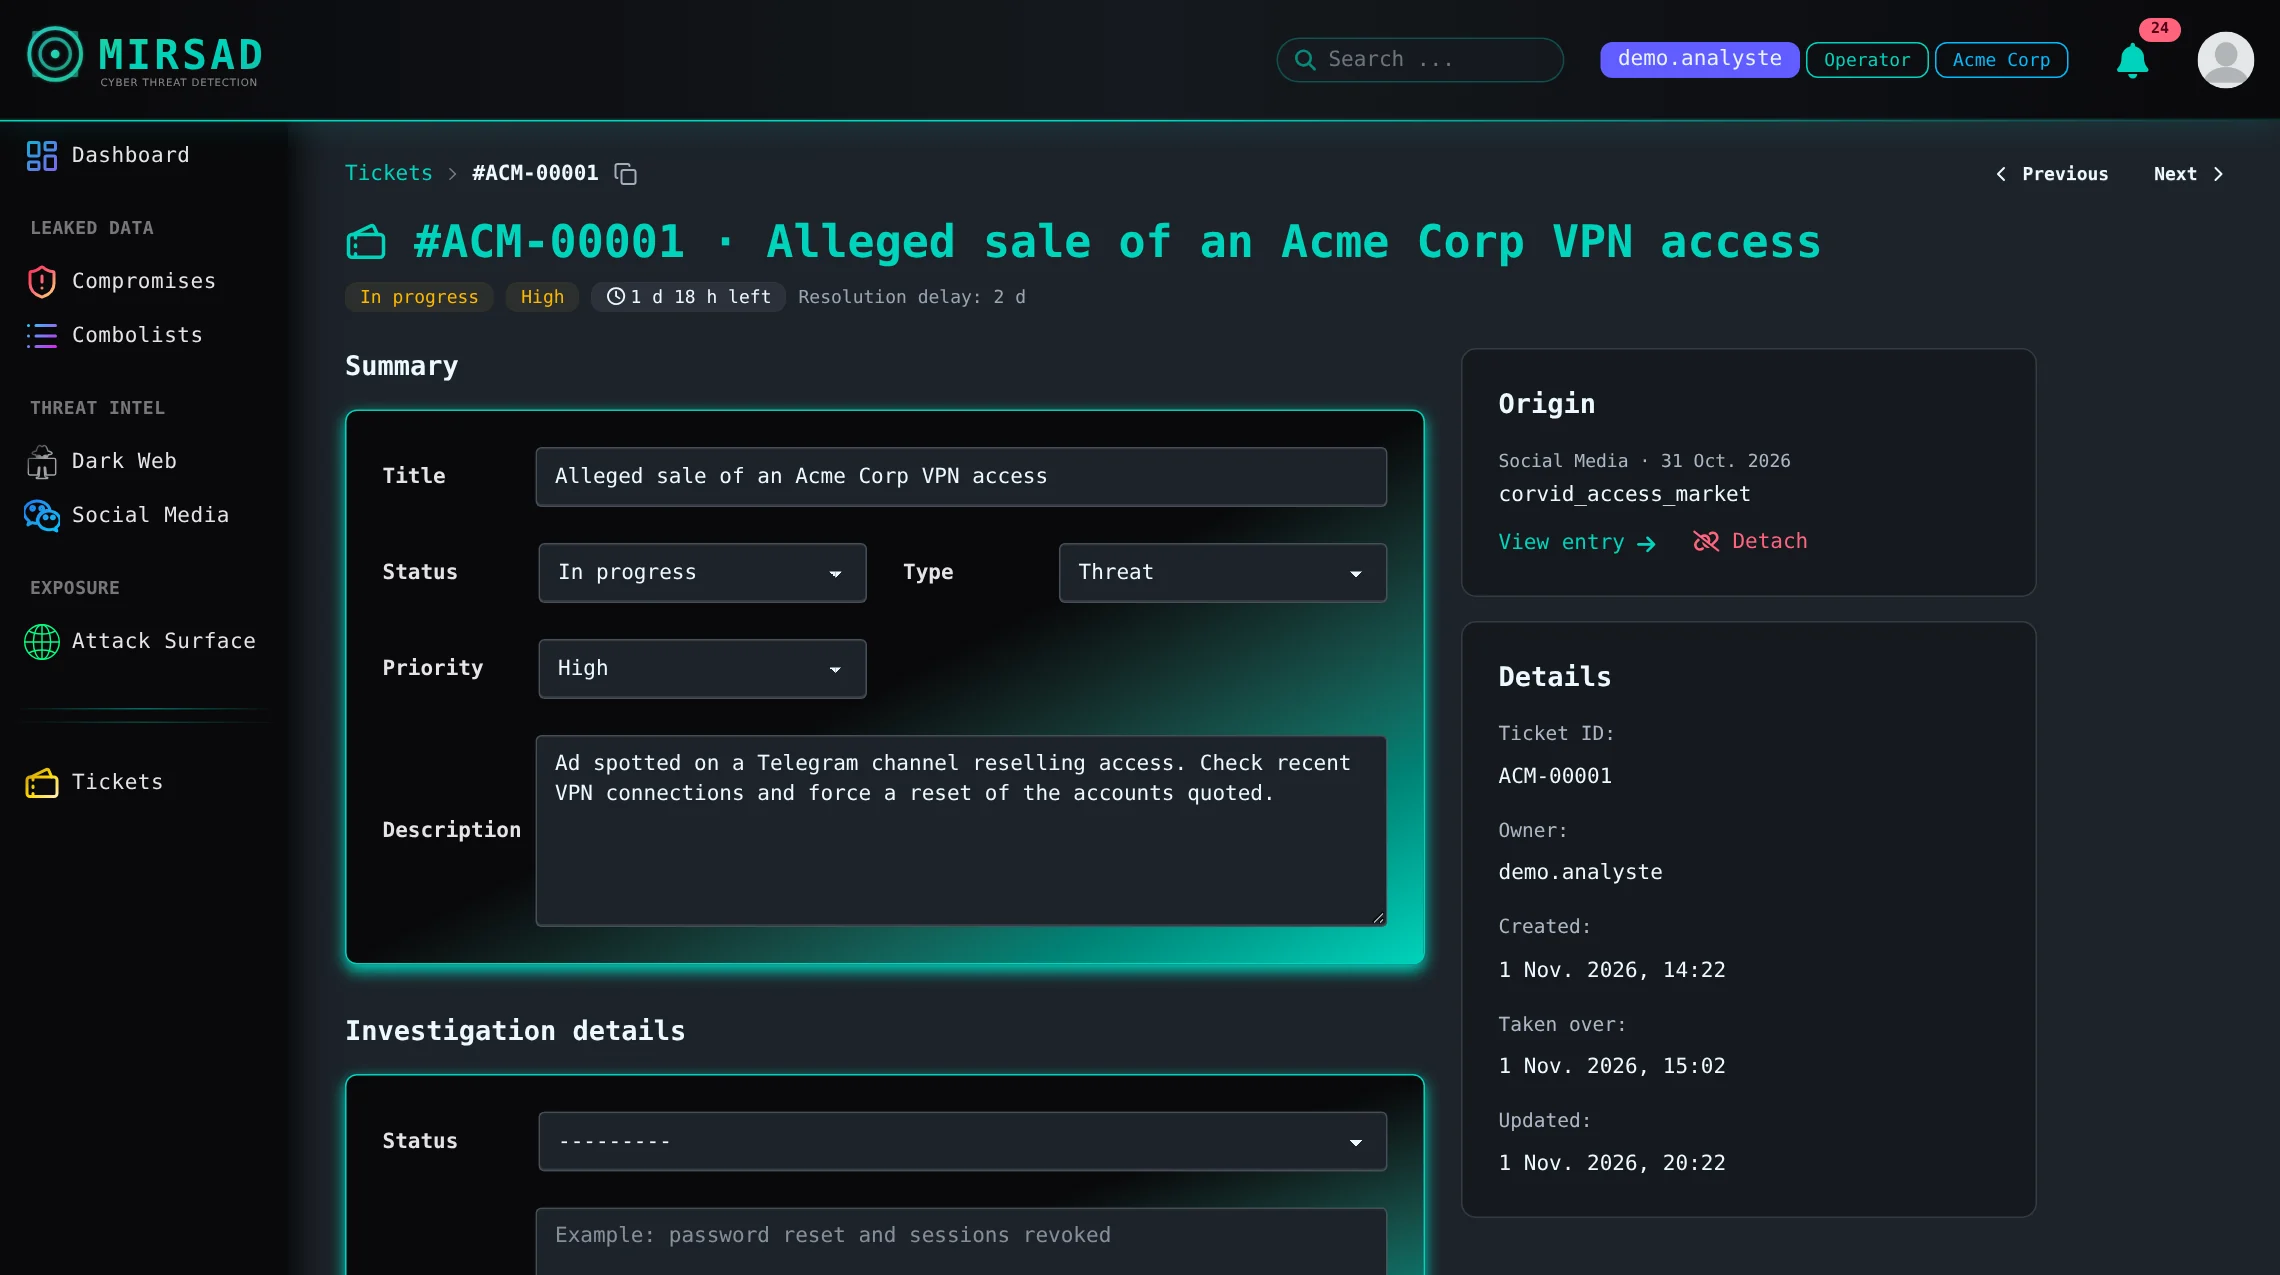
Every incident tracked, through to remediation

Created from the alert, the ticket follows the incident from taking over to closure. Its delays are measured against the SLAs set for your organization.

  1. 1 Priority and time left, measured against your SLAs
  2. 2 The original alert the ticket was created from
  3. 3 Investigation follow-up, through to the closure status
Detail of a ticket in Mirsad, with its priority, its deadline and its original alert

Security by Design

Enterprise-grade security built into every layer of the platform.

Encryption at Rest
All sensitive data encrypted with industry-standard AES encryption
RBAC & Audit Trail
Role-based access control with immutable audit logs for every action
HTTPS + CSP
TLS encryption in transit with strict Content Security Policy headers
API & Webhooks
REST API + HMAC-signed webhooks for SIEM/SOAR integration

Request a Demo

Fill in the form and our team will set up a personalized demo environment within 24 hours.

See the business plans

What we do with your data